An Introduction to Information Security
National Institute of Standards and Technology
A complete introduction to information security for people who need the whole picture: what security controls do, how threats and risk relate, and how policy, awareness, contingency planning and system life cycle decisions fit together. Plain language throughout, with references for going deeper on each topic.
Loading the book...
Keep reading
-
Next in this topic
Information Security Lecture NotesFull lecture notes from an undergraduate information security course, covering the security problem in computing, elementary cryptography, program and operating system security, database security, network controls, and the legal and ethical side of the field.
Verified PDF · Secure download - Cyber Security Digital Notes
Course notes that introduce the core vocabulary of the field: the CIA triad, vulnerabilities and threats, active and passive attacks, cyber crime and cyber warfare, plus units on cyber forensics, mobile device security and organizational policy.
Verified PDF · Secure download - The Cyber Security Body of Knowledge
The reference map of the whole discipline, organized into nineteen knowledge areas written by specialists in each one, from risk management and human factors to cryptography, malware, forensics, network security and hardware. Over a thousand pages, so treat it as the book you keep returning to rather than read straight through.
Verified PDF · Secure download - The NIST Cybersecurity Framework (CSF) 2.0
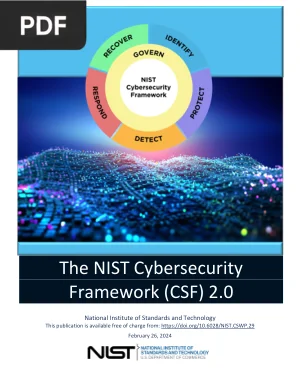
The framework most security programs are now measured against, built around six functions: govern, identify, protect, detect, respond and recover. It explains how to build an organizational profile, set target outcomes, and use tiers to describe how mature your practices actually are.
Verified PDF · Secure download - Guide for Conducting Risk Assessments
A step by step method for assessing risk, covering how to prepare an assessment, identify threat sources and events, determine likelihood and impact, and communicate results so decisions actually get made. Includes the full set of tables and rating scales the process depends on.
Verified PDF · Secure download